Fractional &
Interim CISO
Senior security leadership without the need for a permanent appointment. Governance, executive reporting, strategy and accountable remediation.
Independent senior-level advice to help organisations understand cyber risk, navigate acquisitions and carve-outs, and make meaningful security improvements.
Experienced cyber leadership for periods when the stakes are high, the environment is complex and progress matters more than another report.
Senior security leadership without the need for a permanent appointment. Governance, executive reporting, strategy and accountable remediation.
Identifying material cyber exposure in acquisitions, business separations and carve-outs, then setting credible Day-1 and Day-100 priorities.
Turning security assessments into prioritised delivery, with particular understanding of complex organisations, manufacturing and industrial IT/OT.
From inherited technology and third-party dependencies to Day-1 controls and post-close remediation, I connect cyber findings to the decisions investors and leadership teams need to make.
Explore transaction advisoryExamples are deliberately anonymised to protect client confidentiality. Detailed scope can be discussed where appropriate.
Cyber security assessment and remediation planning within a complex European automotive manufacturing carve-out, including legacy platforms, endpoint protection, access controls and operational dependencies.
Founded and led a specialist cyber security consultancy, combining technical assurance and testing expertise with client engagement, security programme delivery and business leadership.
Specific responsibilities, deliverables and commercial outcomes are discussed only where they can be verified and shared appropriately.
Security advice is most valuable when it connects the real technical position to business priorities and decisions. My approach combines senior leadership perspective with enough practical depth to challenge delivery and track progress.
Start a conversationIdentify the objectives, dependencies, constraints and risks that matter.
Turn technical complexity into choices leadership can act on.
Establish accountable actions, timescales and evidence of improvement.

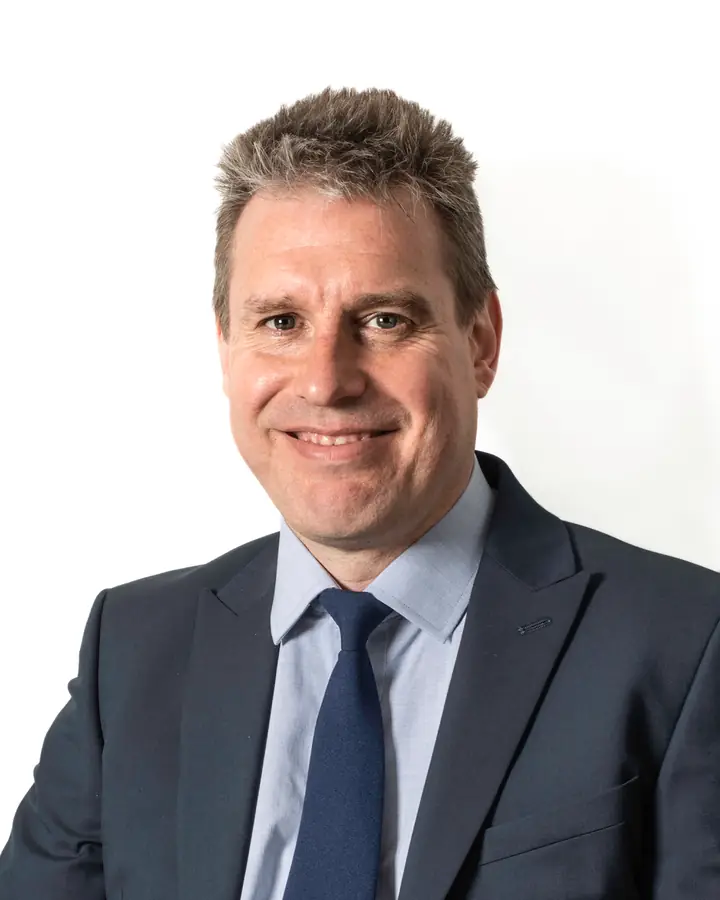
I'm a UK-based cyber security leader and independent adviser with over 20 years' experience across IT leadership, security and technology risk.
My work has spanned security assessment, governance and transformation, with a particular focus on M&A, business carve-outs and industrial environments. I bring practical security knowledge to executive-level challenges: understanding exposure, setting priorities and helping teams deliver.
Postgraduate studies in artificial intelligence inform my developing interest in AI security, risk and governance.
View LinkedIn profileIf you're looking for independent senior cyber security leadership, transaction support or advice on complex security change, I'd welcome a conversation.